API Endpoints

The page provides the possibility to restrict the endpoints of the OMN REST API with access rights permissions. In the left tree the endpoints are structured in Core API and Search API.
API Endpoints allow access right permissions with mandator roles.
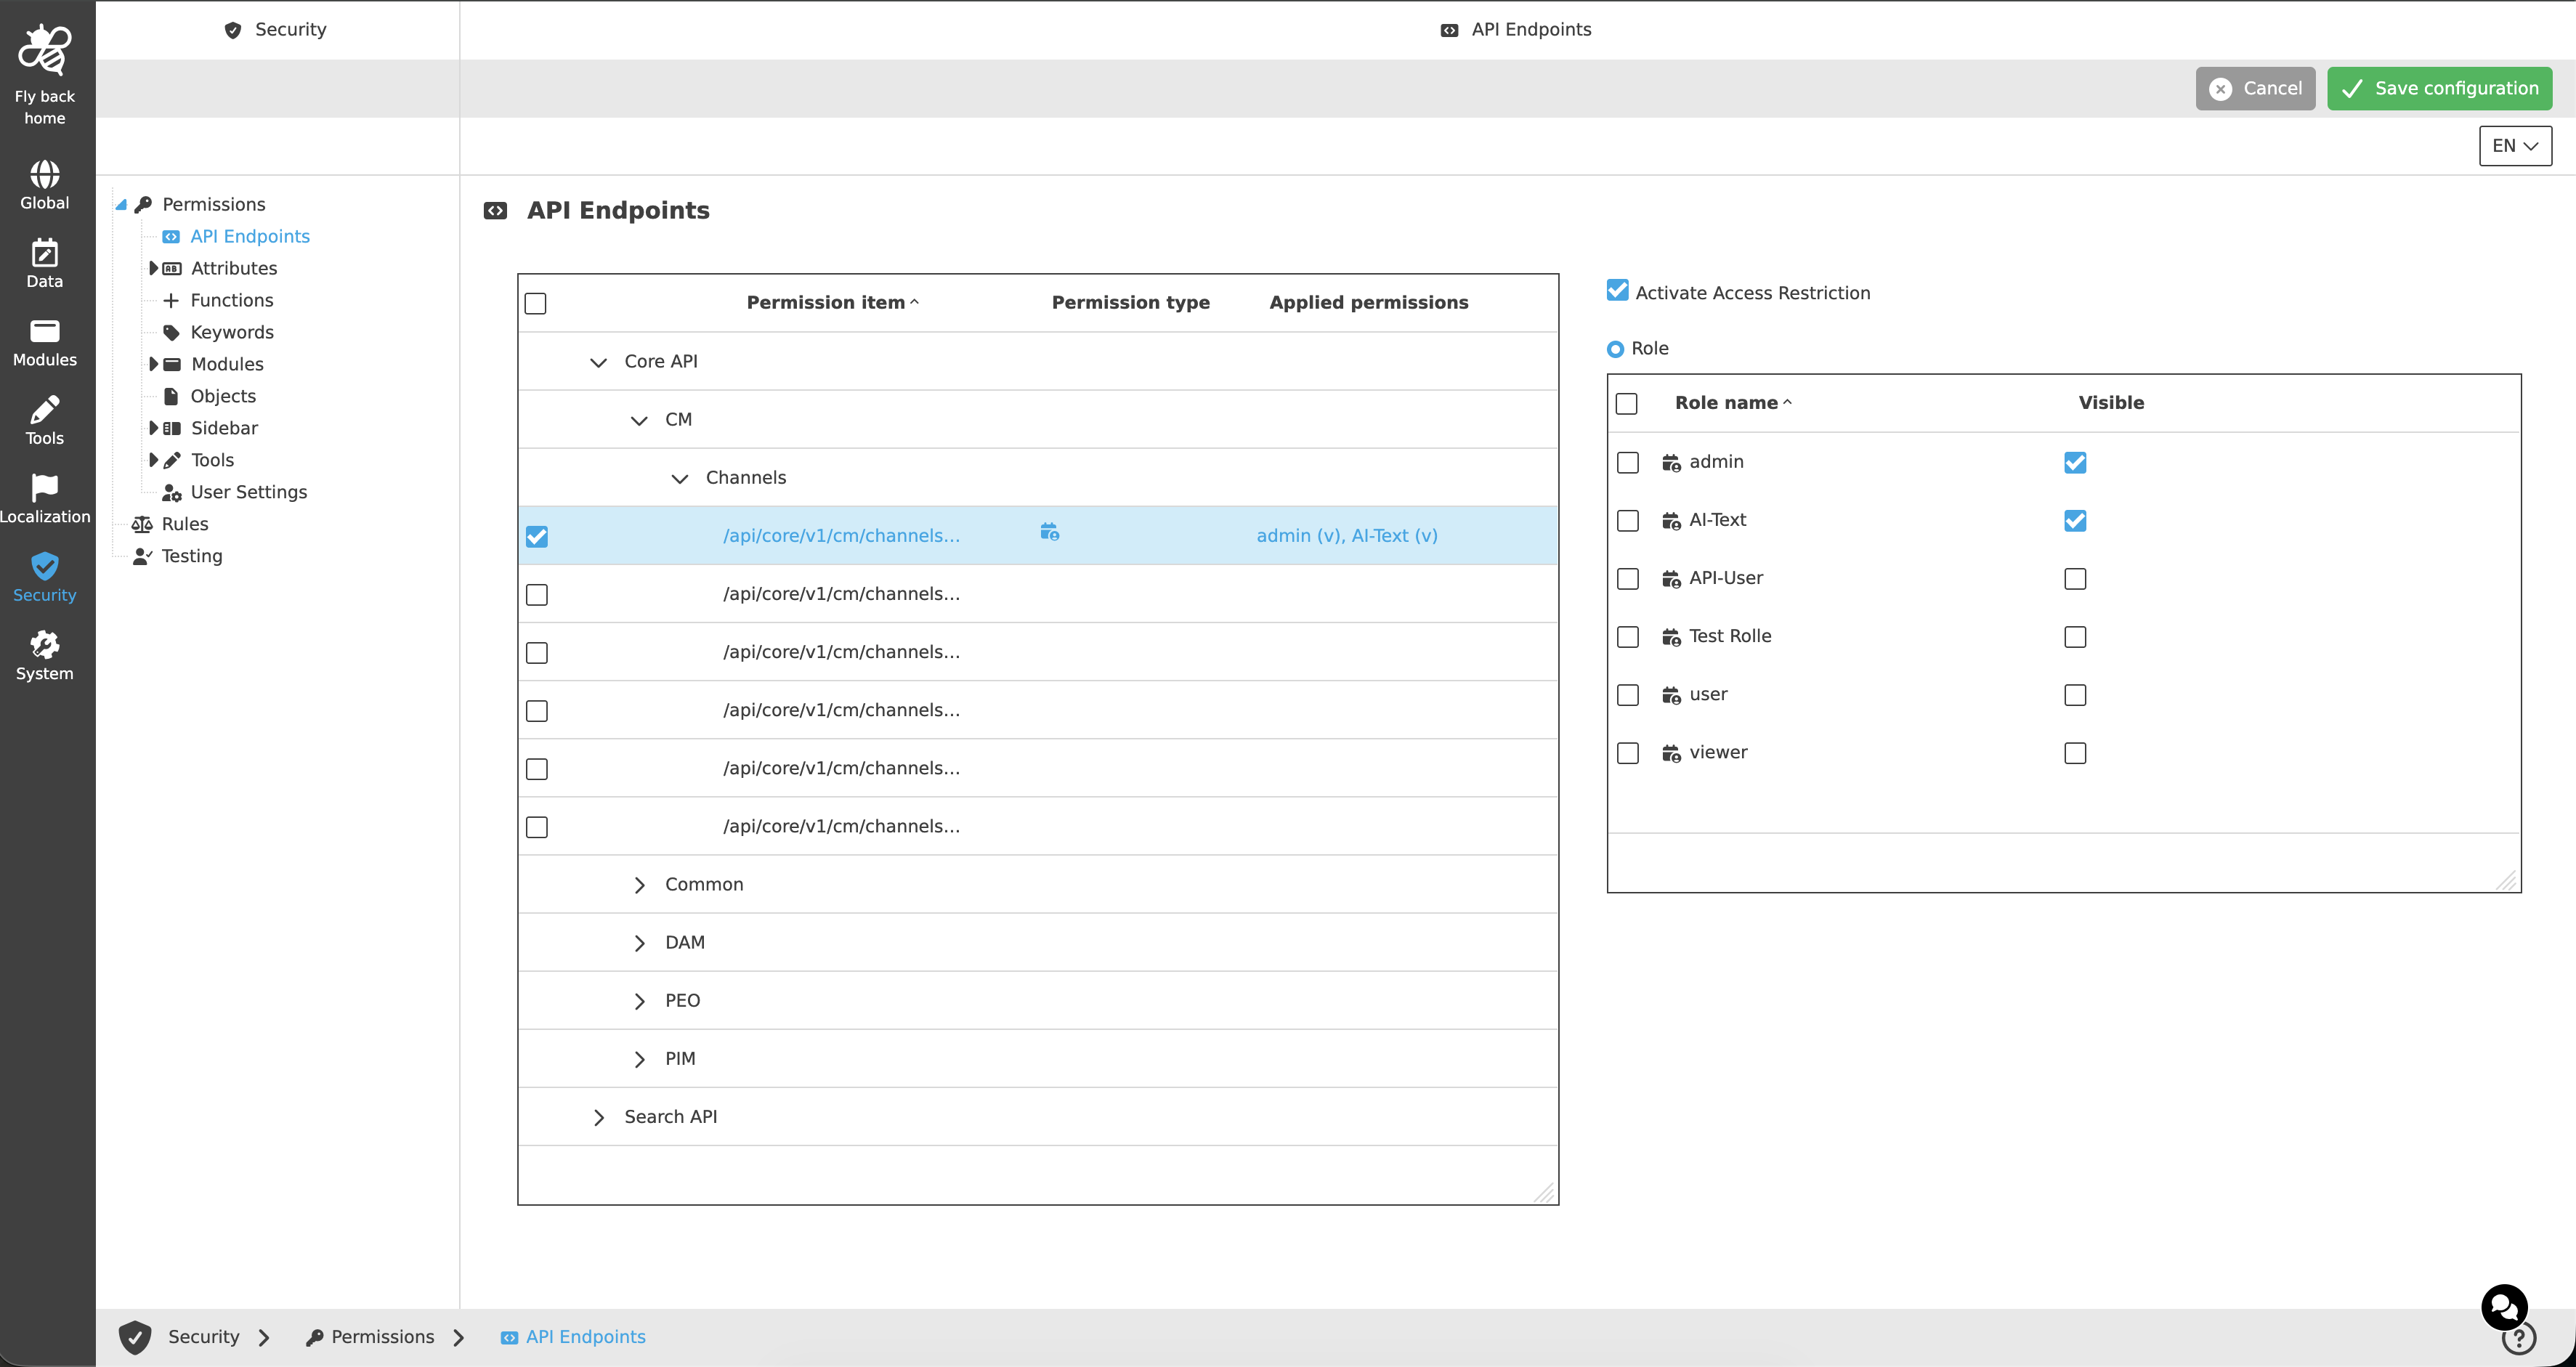
Security permissions api endpoints newCC
Figure 1. Security API Endpoints permission configuration

The following table explains how the permission items are structured for each API:

API Description Note

Core API

Endpoints of the OMN Core API (base path /api/core/v1) are structured in:

  • Domain (CM, Common, DAM, PEO, PIM)

    • API resource (e.g. Channels, Products)

      • Endpoint (e.g. /api/core/v1/pim/products/retrieve)

A description of all Core API endpoints is available in the Core API Endpoint Overview.

Search API

Endpoints of the OMN Search API (base path /api/v1/search) are listed directly below the group:

  • Endpoint (e.g. /api/v1/search/search, /api/v1/search/suggest)

The restriction applies to the endpoint as a whole, independent of the searched index type (e.g. products, assets, channels).

  • API Endpoints can only be restricted with mandator roles. A restriction with rules is not available for API endpoints.

  • Restricted endpoints can only be called by users of the mandator roles marked as 'Visible'. Requests of other users are rejected by the API (HTTP status 403 Forbidden). Make sure that at least one role (e.g. 'admin') keeps access to the endpoints that are needed for your integrations.

  • The restriction is evaluated for every consumer of the OMN REST API, e.g. external integrations, the OMN Companion and MCP tools.

  • The access restriction for API endpoints controls the access to the endpoint itself. Object- and attribute-based permissions on the returned data are configured via Objects and Attributes.

Welcome to the AI Chat!

Write a prompt to get started...